

Excellent FCSS_SASE_AD-25 Updated 2026 Dumps With 100% Exam Passing Guarantee
Best way to practice test for Fortinet FCSS_SASE_AD-25
Fortinet FCSS_SASE_AD-25 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 14
A customer wants to ensure secure access for private applications for their users by replacing their VPN.
Which two SASE technologies can you use to accomplish this task? (Choose two.)
- A. SD-WAN on-ramp
- B. secure SD-WAN
- C. secure web gateway (SWG) and cloud access security broker (CASB)
- D. zero trust network access (ZTNA)
Answer: A,D
Explanation:
ZTNA replaces traditional VPNs by enforcing identity- and posture-based access to private applications. SD- WAN on-ramp integrates with FortiSASE to securely route traffic from branch users to private applications over the SASE fabric, ensuring secure and optimized access.
NEW QUESTION # 15
In the Secure Private Access (SPA) use case, which two FortiSASE features facilitate access to corporate applications? (Choose two.)
- A. thin edge
- B. cloud access security broker (CASB)
- C. zero trust network access (ZTNA)
- D. SD-WAN
Answer: C,D
Explanation:
SD-WAN allows efficient and secure routing of traffic from users to corporate applications, while ZTNA enables secure access control and verification for users connecting to internal resources, both of which are essential for Secure Private Access (SPA) in FortiSASE.
NEW QUESTION # 16
When accessing the FortiSASE portal for the first time, an administrator must select data center locations for which three FortiSASE components? (Choose three.)
- A. Endpoint management
- B. SD-WAN hub
- C. Points of presence
- D. Authentication
- E. Logging
Answer: A,C,E
Explanation:
When accessing the FortiSASE portal for the first time, an administrator must select data center locations for the following FortiSASE components:
Endpoint Management:
The data center location for endpoint management ensures that endpoint data and policies are managed and stored within the chosen geographical region.
Points of Presence (PoPs):
Points of Presence (PoPs) are the locations where FortiSASE services are delivered to users. Selecting PoP locations ensures optimal performance and connectivity for users based on their geographical distribution.
Logging:
The data center location for logging determines where log data is stored and managed. This is crucial for compliance and regulatory requirements, as well as for efficient log analysis and reporting.
FortiOS 7.2 Administration Guide: Details on initial setup and configuration steps for FortiSASE.
FortiSASE 23.2 Documentation: Explains the importance of selecting data center locations for various FortiSASE components.
NEW QUESTION # 17
Which two advantages does FortiSASE bring to businesses with microbranch offices that have FortiAP deployed for unmanaged devices? (Choose two.)
- A. It uses zero trust network access (ZTNA) tags to perform device compliance checks.
- B. It secures internet access both on and off the network.
- C. It simplifies management and provisioning.
- D. It eliminates the requirement for an on-premises firewall.
Answer: B,C
Explanation:
FortiSASE extends secure internet access to users regardless of their location and streamlines the management and provisioning of security policies and services for microbranch offices with unmanaged devices.
NEW QUESTION # 18
Which secure internet access (SIA) use case minimizes individual workstation or device setup, because you do not need to install FortiClient on endpoints or configure explicit web proxy settings on web browser-based end points?
- A. SIA for inline-CASB users
- B. SIA for agentless remote users
- C. SIA for SSLVPN remote users
- D. SIA for site-based remote users
Answer: B
Explanation:
The Secure Internet Access (SIA) use case that minimizes individual workstation or device setup is SIA for agentless remote users. This use case does not require installing FortiClient on endpoints or configuring explicit web proxy settings on web browser-based endpoints, making it the simplest and most efficient deployment.
SIA for Agentless Remote Users:
Agentless deployment allows remote users to connect to the SIA service without needing to install any client software or configure browser settings.
This approach reduces the setup and maintenance overhead for both users and administrators.
Minimized Setup:
Without the need for FortiClient installation or explicit proxy configuration, the deployment is straightforward and quick.
Users can securely access the internet with minimal disruption and administrative effort.
FortiOS 7.2 Administration Guide: Details on different SIA deployment use cases and configurations.
FortiSASE 23.2 Documentation: Explains how SIA for agentless remote users is implemented and the benefits it provides.
NEW QUESTION # 19
Which statement best describes the Digital Experience Monitor (DEM) feature on FortiSASE?
- A. It provides end-to-end network visibility from all the FortiSASE security PoPs to a specific SaaS application.
- B. It can be used to request a detailed analysis of the endpoint from the FortiGuard team.
- C. It requires a separate DEM agent to be downloaded from the FortiSASE portal and installed on the endpoint.
- D. It can help IT and security teams ensure consistent security monitoring for remote users.
Answer: A
Explanation:
The Digital Experience Monitor (DEM) feature in FortiSASE is designed to provide end-to-end network visibility by monitoring the performance and health of connections between FortiSASE security Points of Presence (PoPs) and specific SaaS applications. This ensures that administrators can identify and troubleshoot issues related to latency, jitter, packet loss, and other network performance metrics that could impact user experience when accessing cloud-based services.
Here's why the other options are incorrect:
B . It can be used to request a detailed analysis of the endpoint from the FortiGuard team: This is incorrect because DEM focuses on network performance monitoring, not endpoint analysis. Endpoint analysis would typically involve tools like FortiClient or FortiEDR, not DEM.
C . It requires a separate DEM agent to be downloaded from the FortiSASE portal and installed on the endpoint: This is incorrect because DEM operates at the network level and does not require an additional agent to be installed on endpoints.
D . It can help IT and security teams ensure consistent security monitoring for remote users: While DEM indirectly supports security by ensuring optimal network performance, its primary purpose is to monitor and improve the digital experience rather than enforce security policies.
Fortinet FCSS FortiSASE Documentation - Digital Experience Monitoring Overview FortiSASE Administration Guide - Configuring DEM
NEW QUESTION # 20
Which information does FortiSASE use to bring network lockdown into effect on an endpoint?
- A. The number of critical vulnerabilities detected on the endpoint
- B. The connection status of the tunnel to FortiSASE
- C. Zero-day malware detection on endpoint
- D. The security posture of the endpoint based on ZTNA tags
Answer: D
Explanation:
FortiSASE uses ZTNA tags to assess the endpoint's security posture. If the posture is non-compliant based on predefined rules, FortiSASE enforces network lockdown to restrict access accordingly.
NEW QUESTION # 21
What are two benefits of deploying FortiSASE with FortiGate ZTNA access proxy? (Choose two.)
- A. The on-premises FortiGate performs a device posture check.
- B. It offers data center redundancy.
- C. It is ideal for latency-sensitive applications.
- D. It supports both agentless ZTNA and agent-based ZTNA.
Answer: C,D
Explanation:
Deploying FortiSASE with FortiGate ZTNA access proxy enables efficient access to private applications with reduced latency and supports both agentless and agent-based ZTNA methods for flexible access control.
NEW QUESTION # 22
When viewing the daily summary report generated by FortiSASE, the administrator notices that the report contains very little data.
What is a possible explanation for this almost empty report?
- A. The web filter security profile is not set to Monitor.
- B. Digital experience monitoring is not configured.
- C. There are no security profile groups applied to all policies.
- D. Log allowed traffic is set to Security Events for all policies.
Answer: D
Explanation:
The issue of an almost empty daily summary report in FortiSASE can often be traced back to how logging is configured within the system. Specifically, if "Log Allowed Traffic" is set to "Security Events" for all policies, it means that only security-related events (such as threats or anomalies) are being logged, while normal, allowed traffic is not being recorded. Since most traffic in a typical network environment is allowed, this configuration would result in very little data being captured and subsequently reported in the daily summary.
Here's a breakdown of why the other options are less likely to be the cause:
B . There are no security profile groups applied to all policies: While applying security profiles is important for comprehensive protection, their absence does not directly affect the volume of data in reports unless specific logging settings are also misconfigured.
C . The web filter security profile is not set to Monitor: This option pertains specifically to web filtering activities. Even if web filtering is not set to monitor mode, other types of traffic and logs should still populate the report.
D . Digital experience monitoring is not configured: Digital Experience Monitoring (DEM) focuses on user experience metrics rather than general traffic logging. Its absence would not lead to an almost empty report.
To resolve this issue, administrators should review the logging settings across all policies and ensure that "Log Allowed Traffic" is appropriately configured to capture the necessary data for reporting purposes.
Fortinet FCSS FortiSASE Documentation - Reporting and Logging Best Practices FortiSASE Administration Guide - Configuring Logging Settings
NEW QUESTION # 23
Which statement best describes the Digital Experience Monitor (DEM) feature on FortiSASE?
- A. It provides end-to-end network visibility from all the FortiSASE security PoPs to a specific SaaS application.
- B. It gathers all the vulnerability information from all the FortiClient endpoints.
- C. It is used for performing device compliance checks on endpoints.
- D. It monitors the FortiSASE POP health based on ping probes.
Answer: A
Explanation:
The Digital Experience Monitor (DEM) in FortiSASE measures and monitors network performance from the FortiSASE Points of Presence (PoPs) to specific SaaS or cloud applications, helping identify and troubleshoot performance issues across the service path.
NEW QUESTION # 24
Refer to the exhibit.
While reviewing the traffic logs, the FortiSASE administrator notices that the usernames are showing random characters.
Why are the usernames showing random characters?
- A. FortiSASE uses FortiClient unique identifiers for usernames.
- B. Special characters are used in usernames.
- C. Log anonymization is turned on to hash usernames.
- D. Users are using a shared single sign-on SSO username.
Answer: C
Explanation:
The usernames appear as random character strings because log anonymization is enabled in FortiSASE, which hashes sensitive user information such as usernames to protect privacy while still allowing log analysis.
NEW QUESTION # 25
Refer to the exhibit.
The daily report for application usage for internet traffic shows an unusually high number of unknown applications by category.
What are two possible explanations for this? (Choose two.)
- A. Certificate inspection is not being used to scan application traffic.
- B. Deep inspection is not being used to scan traffic.
- C. The private access policy must be to set to log Security Events.
- D. The inline-CASB application control profile does not have application categories set to Monitor.
Answer: A,B
NEW QUESTION # 26
Which two components are part of onboarding a secure web gateway (SWG) endpoint for secure internet access (SIA)? (Choose two.)
- A. proxy auto-configuration (PAC) file
- B. FortiSASE certificate authority (CA) certificate
- C. FortiClient software
- D. tunnel policy
Answer: A,C
Explanation:
A PAC file is used to redirect client web traffic through the SWG, and FortiClient software is required to connect endpoints to the FortiSASE service for secure internet access (SIA).
NEW QUESTION # 27
What is required to enable the MSSP feature on FortiSASE?
- A. MSSP user accounts and permissions must be configured on the FortiSASE portal.
- B. Role-based access control (RBAC) must be assigned to identity and access management (IAM) users using the FortiCloud IAM portal.
- C. The MSSP add-on license must be applied to FortiSASE.
- D. Multi-tenancy must be enabled on the FortiSASE portal.
Answer: B
Explanation:
To enable the MSSP feature on FortiSASE, you must use the FortiCloud IAM portal to assign RBAC permissions to users. This grants appropriate access to manage multiple tenants or customer accounts securely.
NEW QUESTION # 28
Refer to the exhibit.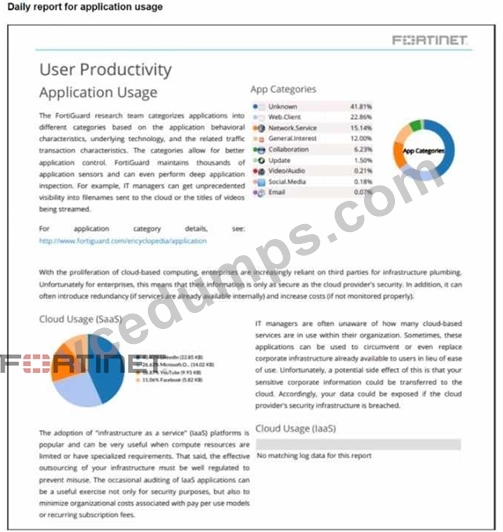
The daily report for application usage shows an unusually high number of unknown applications by category. What are two possible explanations for this? (Choose two.)
- A. Deep inspection is not being used to scan traffic.
- B. Certificate inspection is not being used to scan application traffic.
- C. The inline-CASB application control profile does not have application categories set to Monitor
- D. Zero trust network access (ZTNA) tags are not being used to tag the correct users.
Answer: A,C
NEW QUESTION # 29
Which two components are part of onboarding a secure web gateway (SWG) endpoint? (Choose two)
- A. proxy auto-configuration (PAC) file
- B. FortiSASE CA certificate
- C. FortiClient installer
- D. FortiSASE invitation code
Answer: A,B
Explanation:
Onboarding a Secure Web Gateway (SWG) endpoint involves several components to ensure secure and effective integration with FortiSASE. Two key components are the FortiSASE CA certificate and the proxy auto-configuration (PAC) file.
FortiSASE CA Certificate:
The FortiSASE CA certificate is essential for establishing trust between the endpoint and the FortiSASE infrastructure.
It ensures that the endpoint can securely communicate with FortiSASE services and inspect SSL/TLS traffic.
Proxy Auto-Configuration (PAC) File:
The PAC file is used to configure the endpoint to direct web traffic through the FortiSASE proxy.
It provides instructions on how to route traffic, ensuring that all web requests are properly inspected and filtered by FortiSASE.
FortiOS 7.2 Administration Guide: Details on onboarding endpoints and configuring SWG.
FortiSASE 23.2 Documentation: Explains the components required for integrating endpoints with FortiSASE and the process for deploying the CA certificate and PAC file.
NEW QUESTION # 30
A customer needs to implement device posture checks for their remote endpoints while accessing the protected server. They also want the TCP traffic between the remote endpoints and the protected servers to be processed by FortiGate.
In this scenario, which three setups will achieve the above requirements? (Choose three.)
- A. Configure ZTNA tags on FortiGate.
- B. Configure FortiGate as a zero trust network access (ZTNA) access proxy.
- C. Configure ZTNA servers and ZTNA policies on FortiGate.
- D. Configure private access policies on FortiSASE with ZTNA.
- E. Sync ZTNA tags from FortiSASE to FortiGate.
Answer: A,B,C
Explanation:
To meet the requirements of implementing device posture checks for remote endpoints and ensuring that TCP traffic between the endpoints and protected servers is processed by FortiGate, the following three setups are necessary:
Configure ZTNA tags on FortiGate (Option A):
ZTNA (Zero Trust Network Access) tags are used to define access control policies based on the security posture of devices. By configuring ZTNA tags on FortiGate, administrators can enforce granular access controls, ensuring that only compliant devices can access protected resources.
Configure FortiGate as a zero trust network access (ZTNA) access proxy (Option B):
FortiGate can act as a ZTNA access proxy, which allows it to mediate and secure connections between remote endpoints and protected servers. This setup ensures that all TCP traffic passes through FortiGate, enabling inspection and enforcement of security policies.
Configure ZTNA servers and ZTNA policies on FortiGate (Option C):
To enable ZTNA functionality, administrators must define ZTNA servers (the protected resources) and create ZTNA policies on FortiGate. These policies determine how traffic is routed, inspected, and controlled based on device posture and user identity.
Here's why the other options are incorrect:
D . Configure private access policies on FortiSASE with ZTNA: While FortiSASE supports ZTNA, the requirement specifies that TCP traffic must be processed by FortiGate. Configuring private access policies on FortiSASE would route traffic through FortiSASE instead of FortiGate, which does not meet the stated requirements.
E . Sync ZTNA tags from FortiSASE to FortiGate: Synchronizing ZTNA tags is unnecessary in this scenario because the focus is on FortiGate processing the traffic. The tags can be directly configured on FortiGate without involving FortiSASE.
Fortinet FCSS FortiSASE Documentation - Zero Trust Network Access (ZTNA) Deployment FortiGate Administration Guide - ZTNA Configuration
NEW QUESTION # 31
In which three ways does FortiSASE help organizations ensure secure access for remote workers? (Choose three.)
- A. It uses the identity & access management (IAM) portal to validate the identities of remote workers.
- B. It enforces multi-factor authentication (MFA) to validate remote users.
- C. It secures traffic from endpoints to cloud applications.
- D. It offers zero trust network access (ZTNA) capabilities.
- E. It enforces granular access policies based on user identities.
Answer: C,D,E
Explanation:
FortiSASE provides several features to ensure secure access for remote workers. The following three ways are particularly relevant:
It secures traffic from endpoints to cloud applications (Option B):
FortiSASE secures all traffic between remote endpoints and cloud applications by inspecting it in real time. This includes applying security policies, threat detection, and data protection measures to ensure that traffic is safe and compliant.
It offers zero trust network access (ZTNA) capabilities (Option D):
ZTNA ensures that remote workers are granted access to resources based on strict verification of their identity and device posture. By treating all users and devices as untrusted by default, ZTNA minimizes the risk of unauthorized access and lateral movement within the network.
It enforces granular access policies based on user identities (Option E):
FortiSASE allows administrators to define and enforce fine-grained access policies based on user identities, roles, and other attributes. This ensures that remote workers only have access to the resources they need, reducing the attack surface.
Here's why the other options are incorrect:
A . It enforces multi-factor authentication (MFA) to validate remote users: While MFA is a critical security measure, it is typically implemented through identity providers (e.g., FortiAuthenticator or third-party solutions) rather than directly through FortiSASE.
C . It uses the identity & access management (IAM) portal to validate the identities of remote workers: FortiSASE integrates with IAM systems but does not use the IAM portal itself to validate identities. Identity validation is handled through authentication mechanisms like SAML, LDAP, or OAuth.
Fortinet FCSS FortiSASE Documentation - Secure Remote Access
FortiSASE Administration Guide - ZTNA and Access Policies
NEW QUESTION # 32
Which secure internet access (SIA) use case minimizes individual endpoint configuration?
- A. SIA for SSL VPN remote users
- B. SIA using ZTNA
- C. Site-based remote user internet access
- D. Agentless remote user internet access
Answer: D
Explanation:
The agentless remote user internet access use case is designed to minimize individual endpoint configuration. In this scenario, FortiSASE provides secure internet access without requiring the installation of an agent on the endpoint device. This approach is particularly useful for environments with unmanaged devices or temporary users, as it eliminates the need for complex configurations on each endpoint. Instead, security policies are enforced at the network level, ensuring consistent protection without relying on endpoint-specific software.
Here's why the other options are incorrect:
A . Site-based remote user internet access: This use case involves securing internet access for users at a specific site or location, typically through a gateway or firewall. While it simplifies configuration for all users at that site, it does not specifically minimize individual endpoint configuration for remote users.
C . SIA for SSL VPN remote users: SSL VPN requires users to connect to the corporate network via a client or browser-based interface. This approach often involves additional configuration on the endpoint, such as installing and configuring the SSL VPN client.
Fortinet FCSS FortiSASE Documentation - Secure Internet Access (SIA) Use Cases FortiSASE Administration Guide - Agentless Remote User Access D). SIA using ZTNA: Zero Trust Network Access (ZTNA) focuses on verifying the identity and posture of devices before granting access to resources. While ZTNA enhances security, it may require endpoint agents or posture checks, which involve some level of endpoint configuration.
NEW QUESTION # 33
......
FCSS - FortiSASE 25 Administrator Certification Sample Questions and Practice Exam: https://prep4sure.vcedumps.com/FCSS_SASE_AD-25-examcollection.html
